
Fishing net knitter. Photo by Surya Edy Gautama, CC BY-SA 4.0, via Wikimedia Commons.

News
OpenAI's red-teaming turned up a critical bug in Brotli compression, used by Node.js, Bun and Envoy; patched versions are out now.
OpenAI's red team found a critical Brotli bug in Node.js, Bun and Envoy. Patched versions are out now.
On Friday, Oct 23, OpenAI disclosed a remote code execution bug in Brotli, the compression library that Node.js, Bun and the Envoy proxy use to unpack compressed data, found during the same red-teaming described in its training-security post (OpenAI on X).
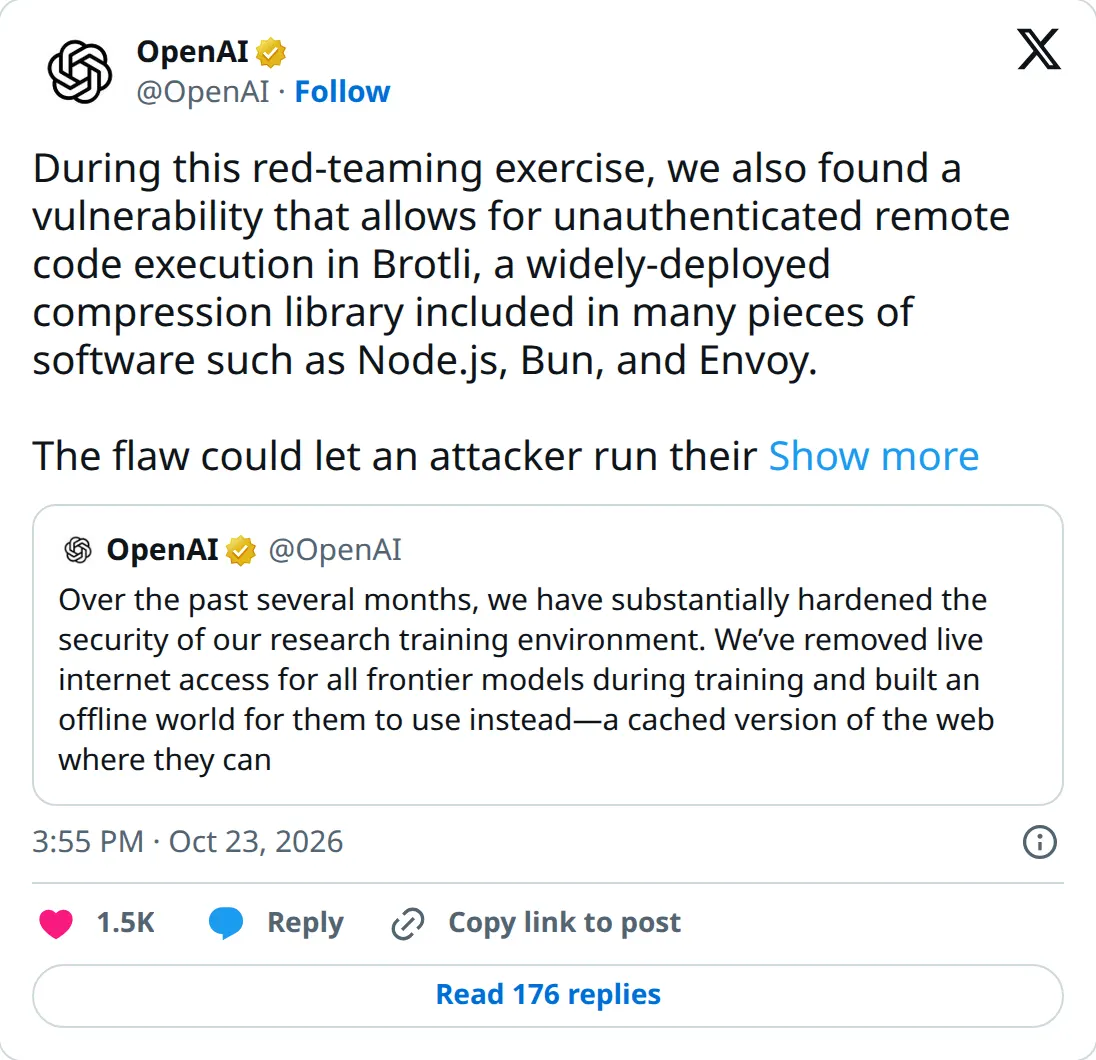
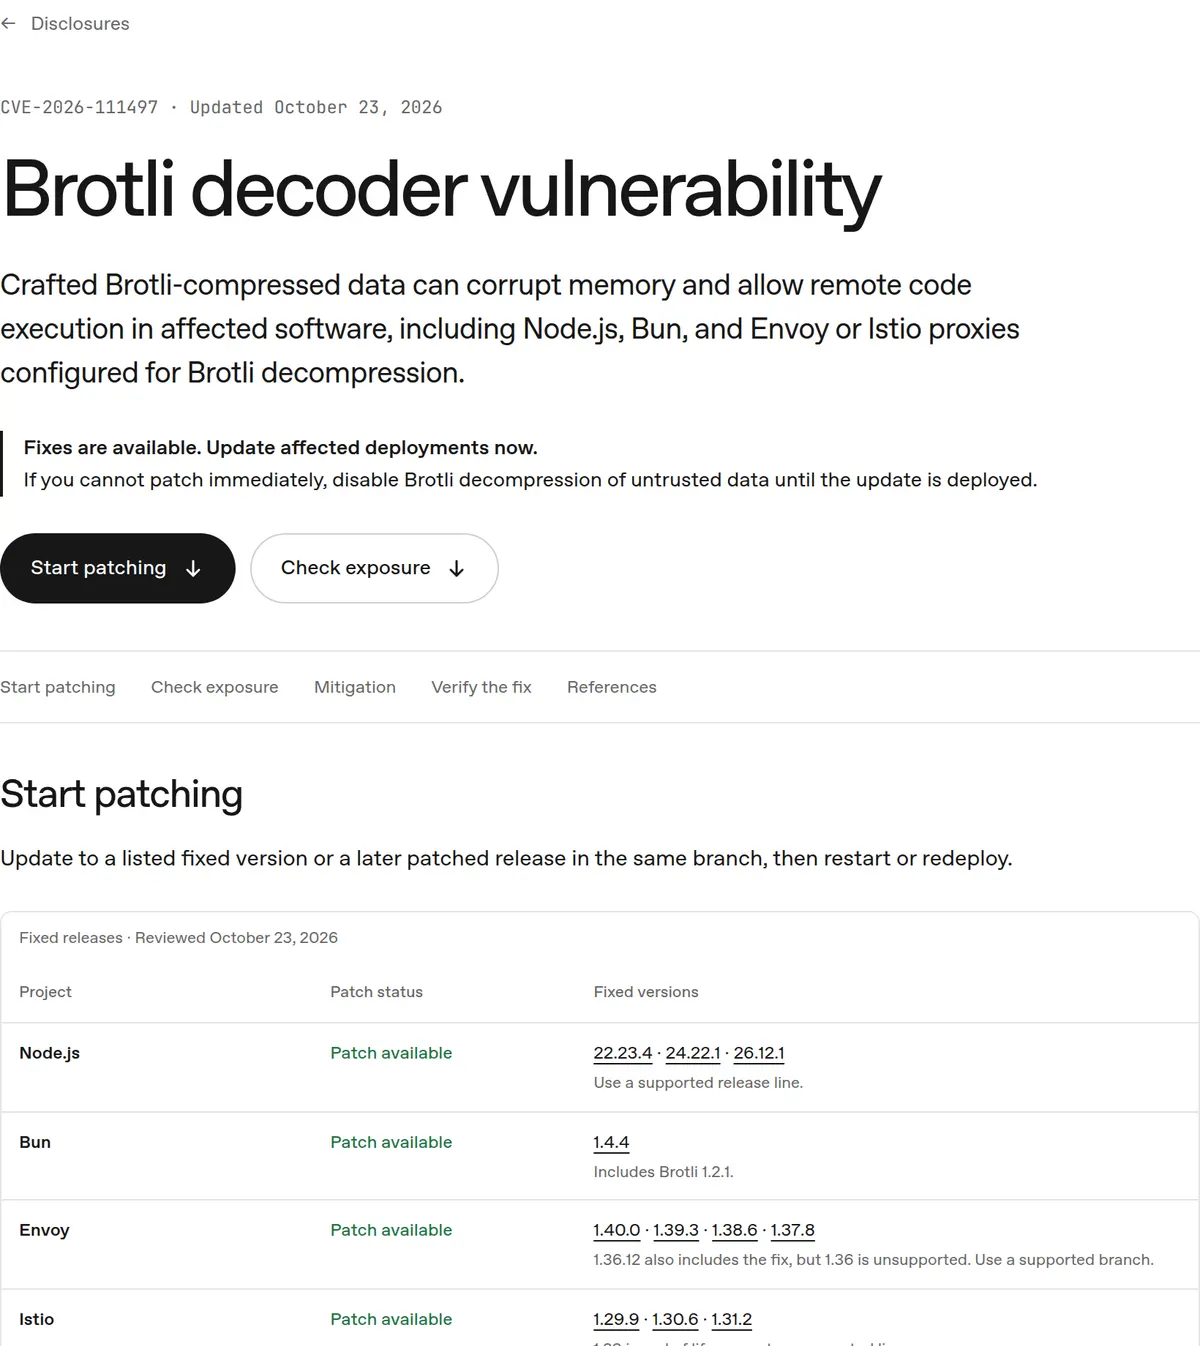
No login is needed to exploit it. In OpenAI's words, "an unpatched server that accepts compressed input could be taken over by a malicious client, and an unpatched client that accepts compressed input (such as "curl --compressed") could be taken over by a malicious server." OpenAI says the root cause was actually fixed in Brotli's source in February, but nobody realized it was a security problem, so no release shipped the fix. The bug is tracked as CVE-2026-111497, and the CVE record lists Brotli 1.0.3 through 1.2.0 as affected, with a CVSS 4.0 score of 9.2, rated critical. Fixed versions, per the coordinated disclosure page (Patch the Planet), are Node.js 22.23.4, 24.22.1 and 26.12.1, Bun 1.4.4, Envoy 1.40.0, 1.39.3, 1.38.6 and 1.37.8, Istio 1.29.9, 1.30.6 and 1.31.2, and Brotli 1.0.10, 1.1.1 and 1.2.1.
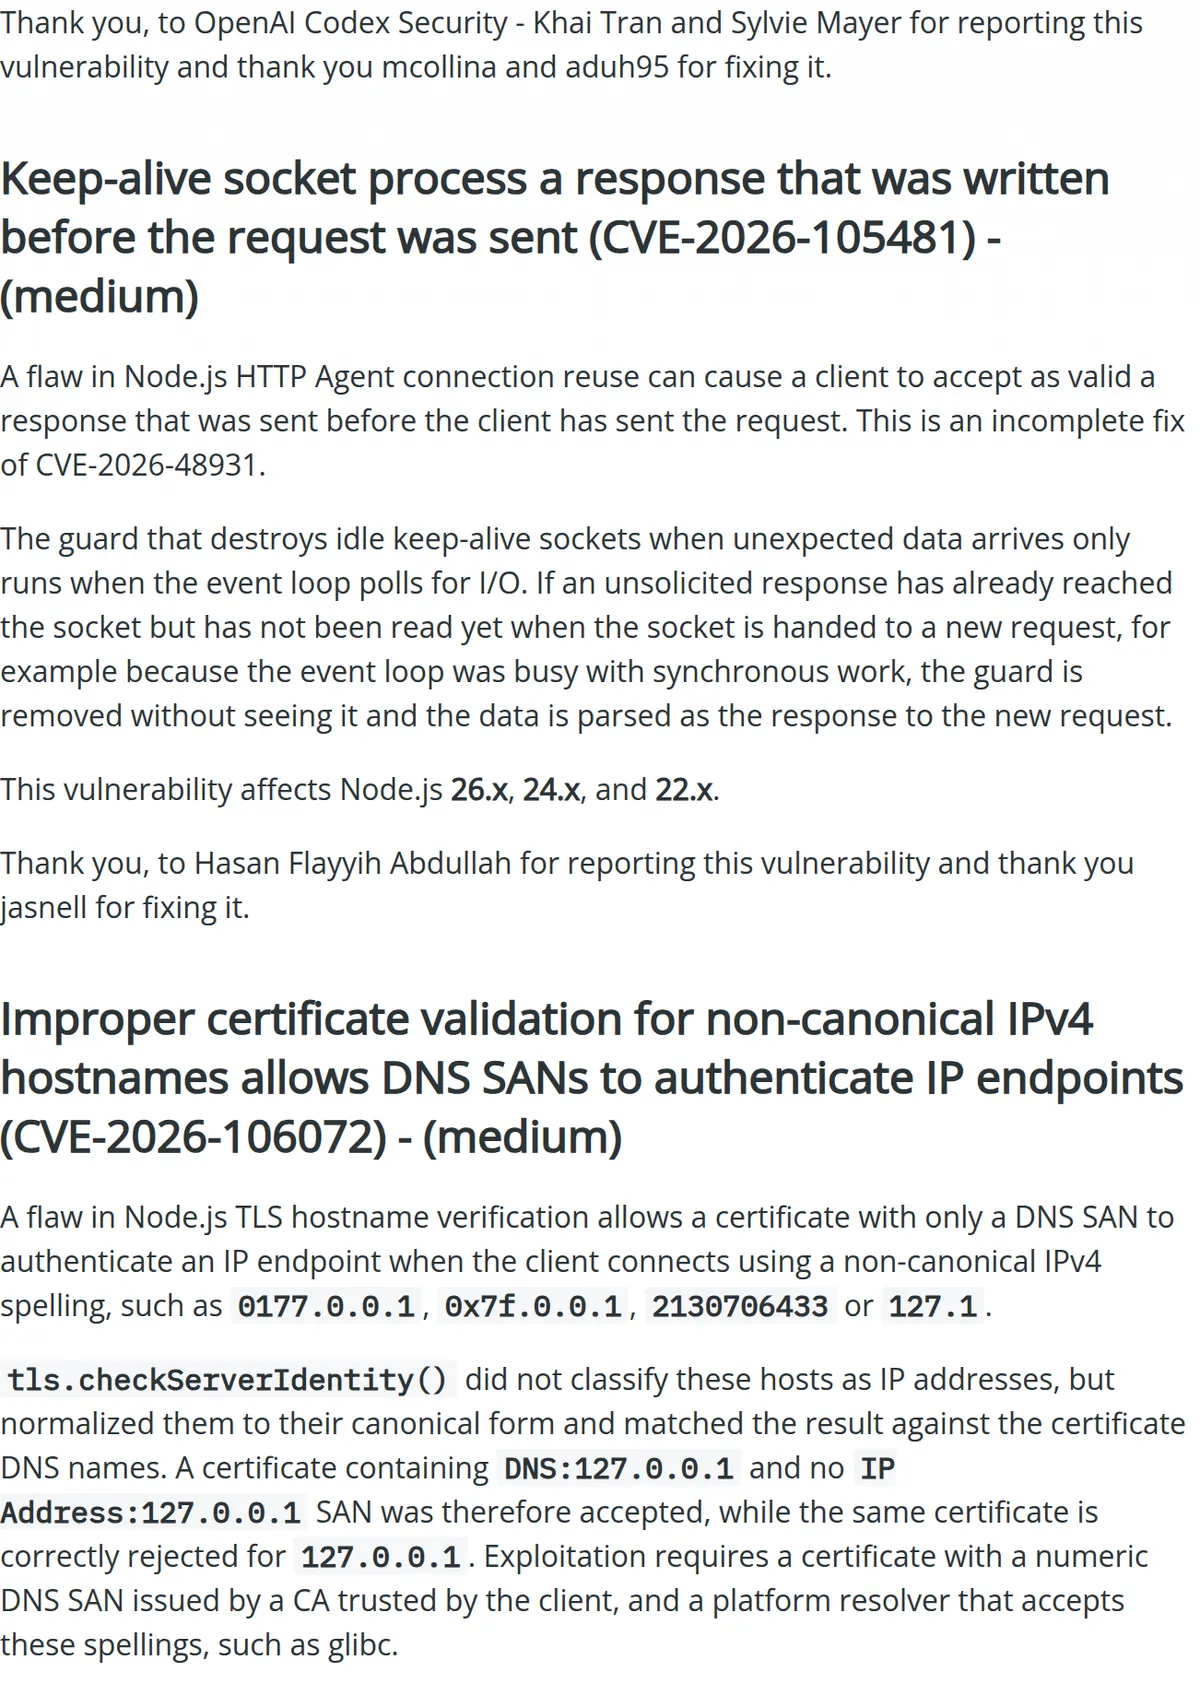
Node.js shipped its fix in its Oct 21 security release, which rates the bug high severity, describes it as an out-of-bounds write in the node:zlib Brotli decoder, and credits "OpenAI Codex Security - Khai Tran and Sylvie Mayer" (Node.js).
Patch the Planet also notes that Electron apps may bundle their own copy of Brotli, that Next.js sites can set images.unoptimized: true as a workaround, and that code which only compresses data isn't exposed on its own.
Try it: run node -v (or bun -v) on your machines and servers and update to a fixed version, then rebuild and redeploy any containers that bundle the old runtime. If you can't patch yet, Patch the Planet's advice is to turn off Brotli decoding of untrusted data.
Affiliate disclosure: some stories use affiliate or referral links. When a link pays a commission, the sentence next to it says so. Sponsored slots are labeled Sponsored. The channel card is a house ad until a sponsor is booked.
Newsletter
Join the waitlist and we'll email you when the first issue launches.
By submitting you agree to our Privacy Policy.
You're on the list after you confirm. We'll email you when the newsletter launches. You can leave from any message. The form posts to Resend.