
Hole in a wire fence. Photo by Santeri Viinamäki, CC BY-SA 4.0, via Wikimedia Commons.

News
AI helped find two critical holes in PHP, the language behind most websites. Update today.
The PHP project released 8.5.12, 8.4.27, 8.3.36 and 8.2.35 to fix two critical flaws that can run code without a login.
On Wednesday, Oct 21, the PHP project released PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35 to fix two critical flaws, CVE-2026-109618 and CVE-2026-109619, each rated 9.2 out of 10. Both can let an attacker run their own code on a web server without logging in (PHP Foundation).
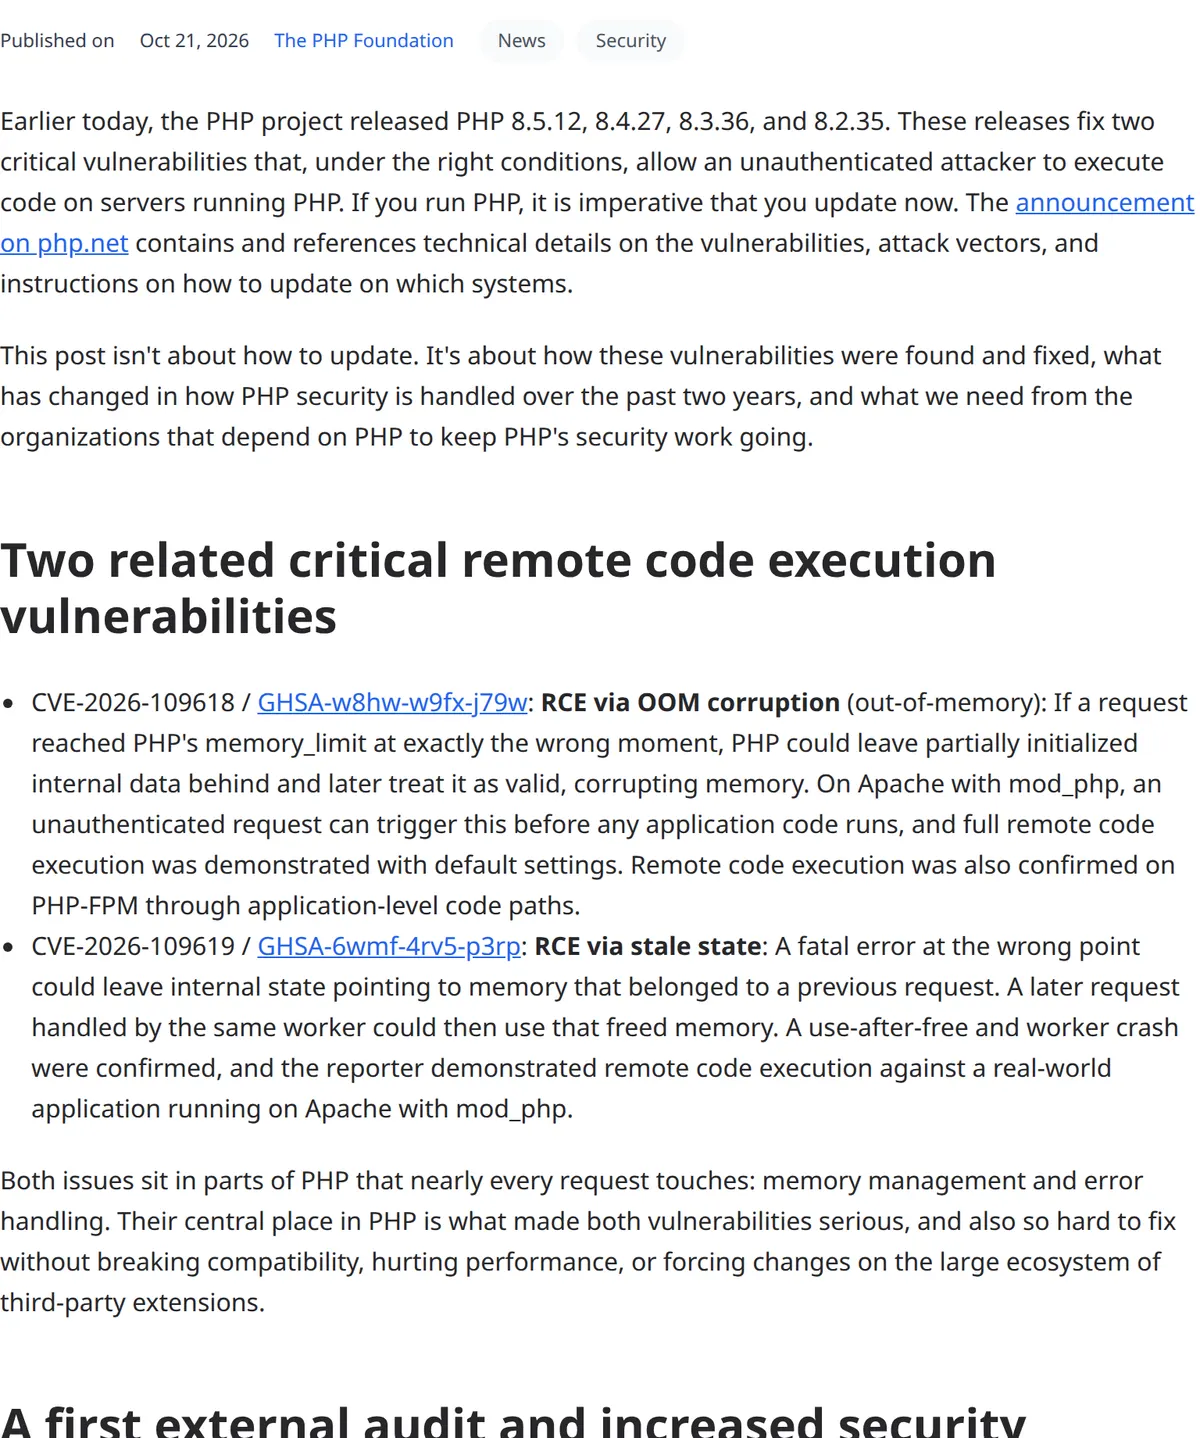
They sit in PHP's core engine, in the memory handling and error handling nearly every request touches, so a site is exposed even when its own code is fine. Wiz says every PHP version back to 5.4 is affected by at least one of them, which reaches WordPress, Drupal and MediaWiki sites (Wiz).
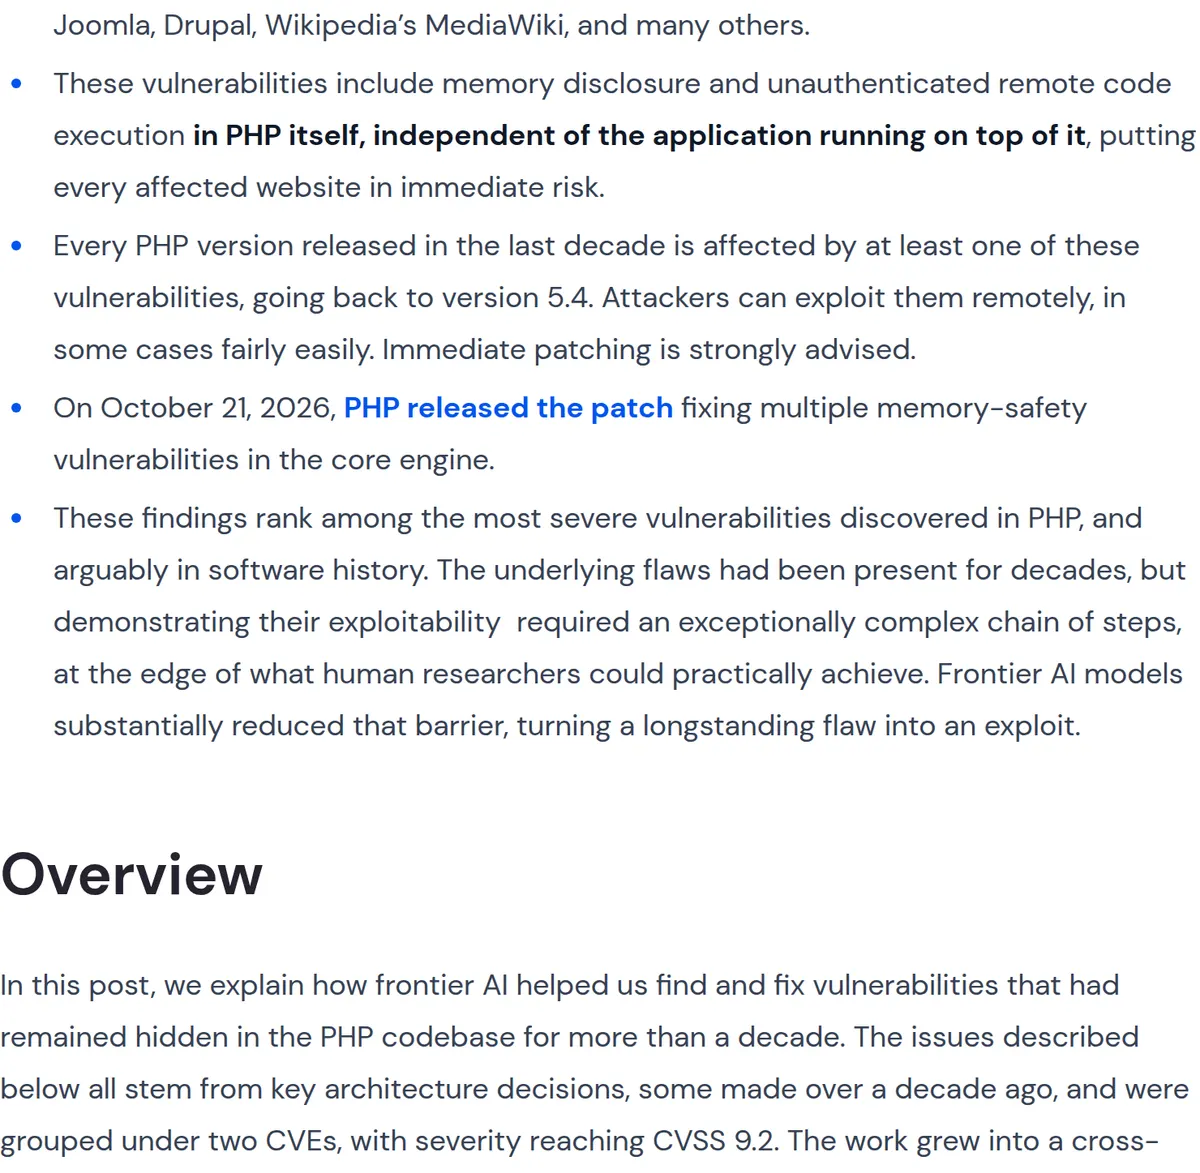
AI did a lot of the finding. Security firm Calif reported the flaw on Aug 11 after finding it with OpenAI's GPT-5.6 Sol through OpenAI's Patch the Planet program, OpenAI reported the same root cause that same day, and Wiz found the flaws on its own using its Wiz Atlas agent, Gemini 4 Argon and GPT-5.6 Sol (OpenAI).
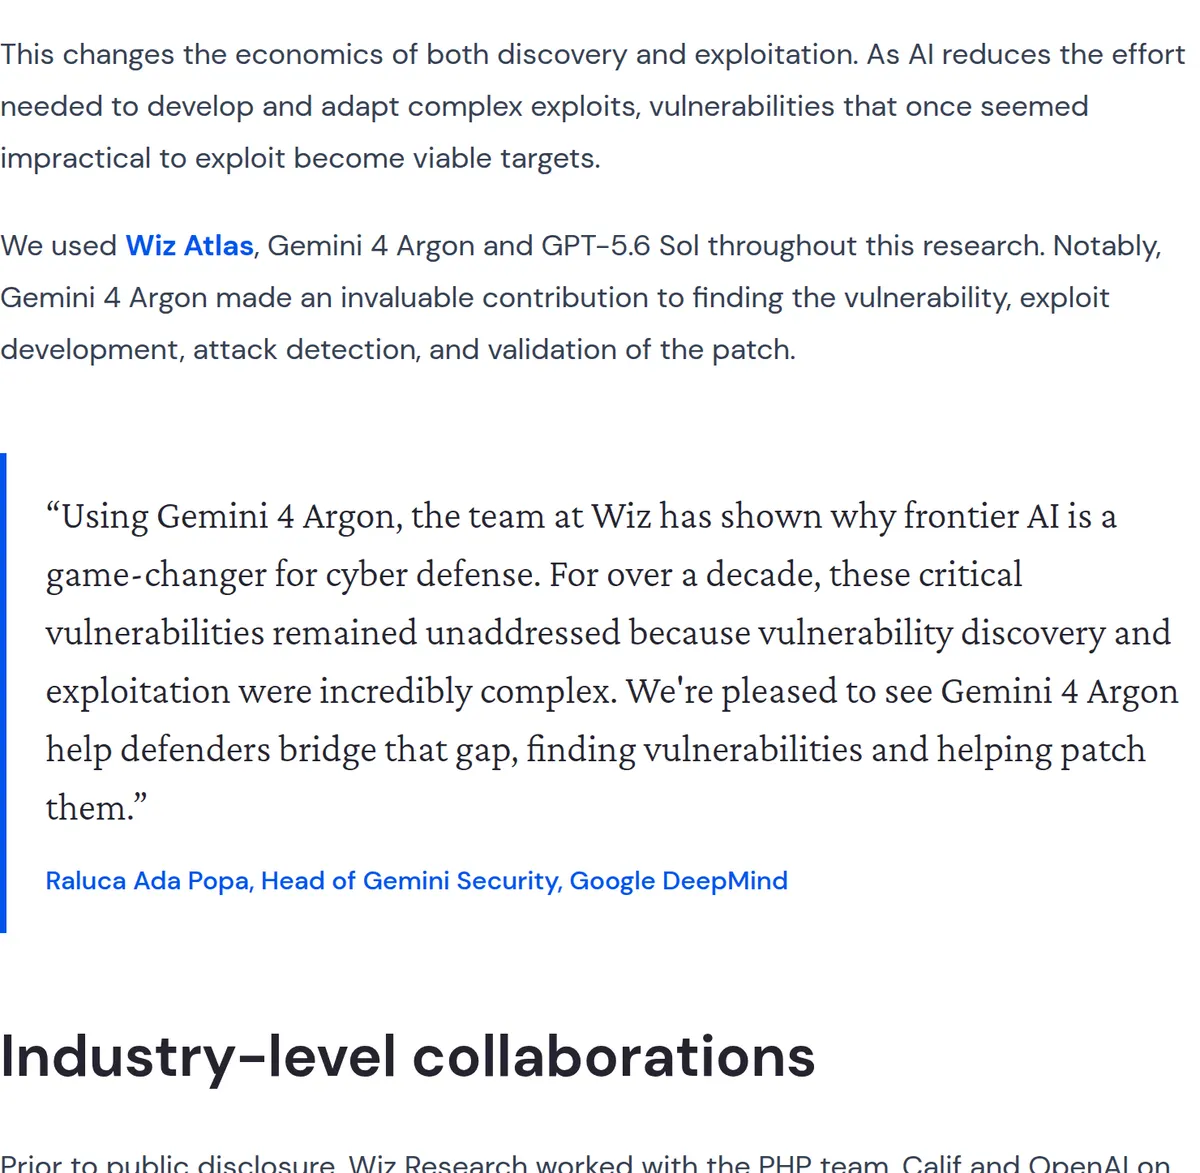
Wiz says AI is also what makes the flaws practical to attack: building a working exploit had been "at the edge of what human researchers could practically achieve." The release came a day early after the bug IDs leaked online Tuesday, and the PHP Foundation says the fix had stalled for months after its developers first saw signs of the problem in 2024.
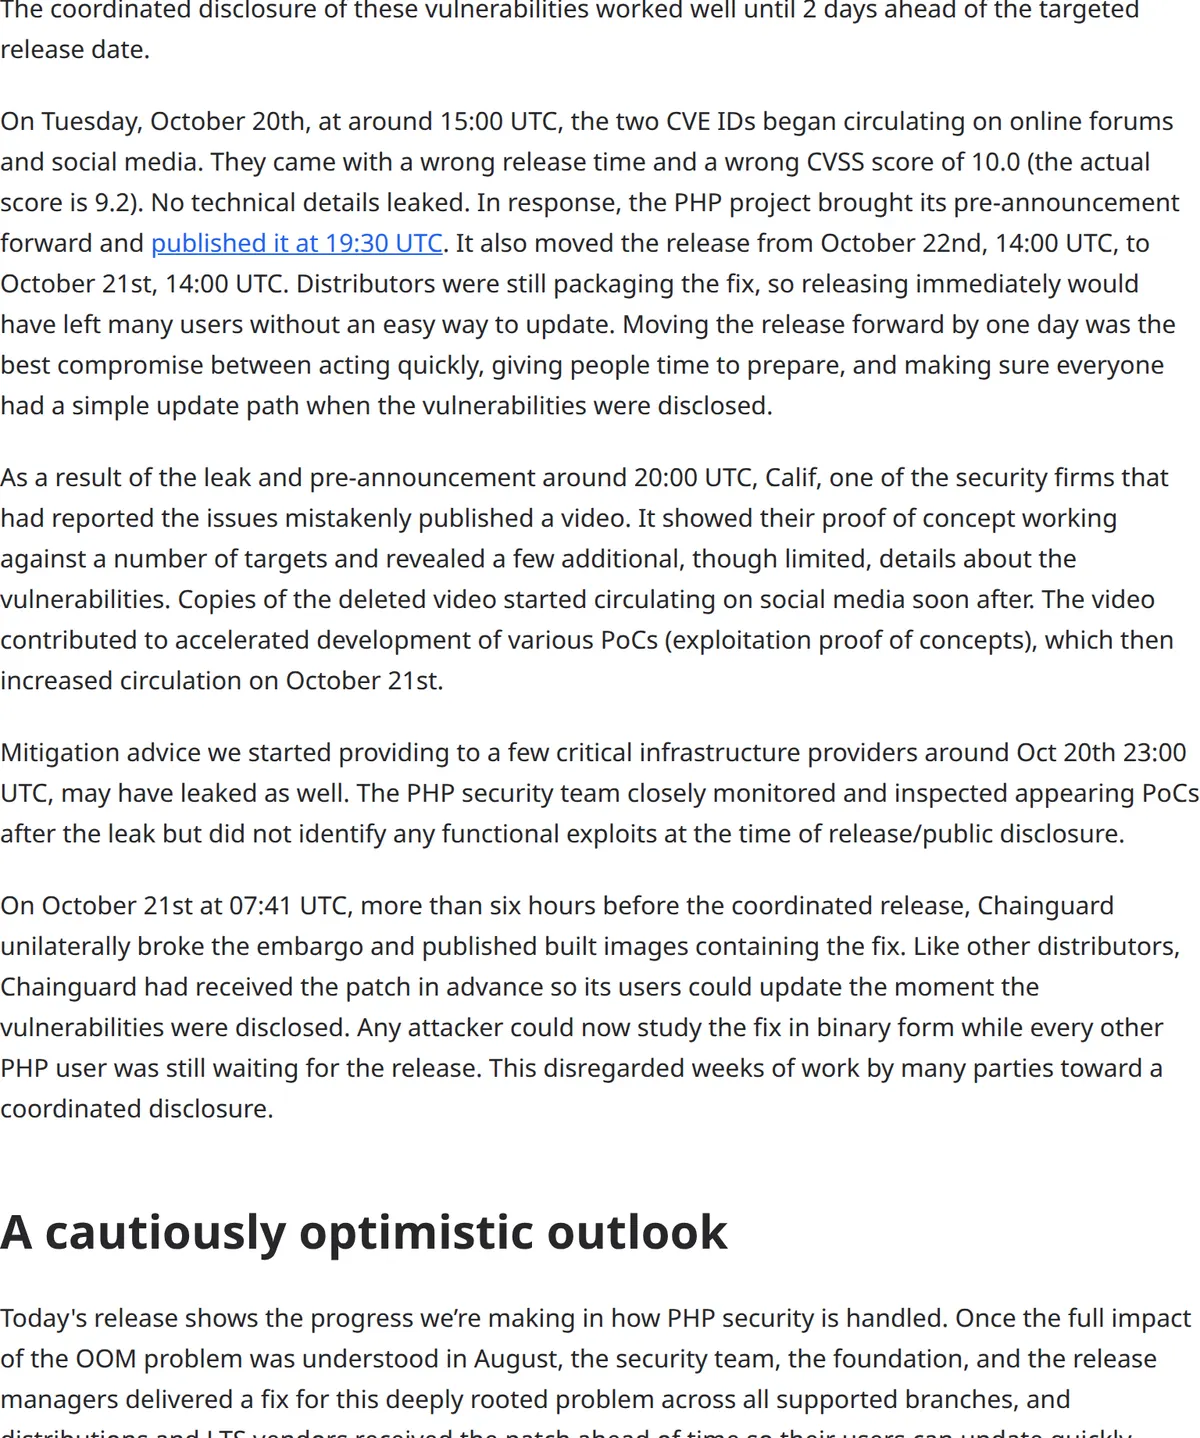
The NSA, the UK's National Cyber Security Centre and CERT-EU told anyone who can't patch right away to consider taking their sites offline. BBC News reports that Finland took down government web services and that Wikimedia took some systems offline as a precaution, and Cloudflare's CTO said it was "seeing early attacks emerging" (BBC News, CERT-EU).
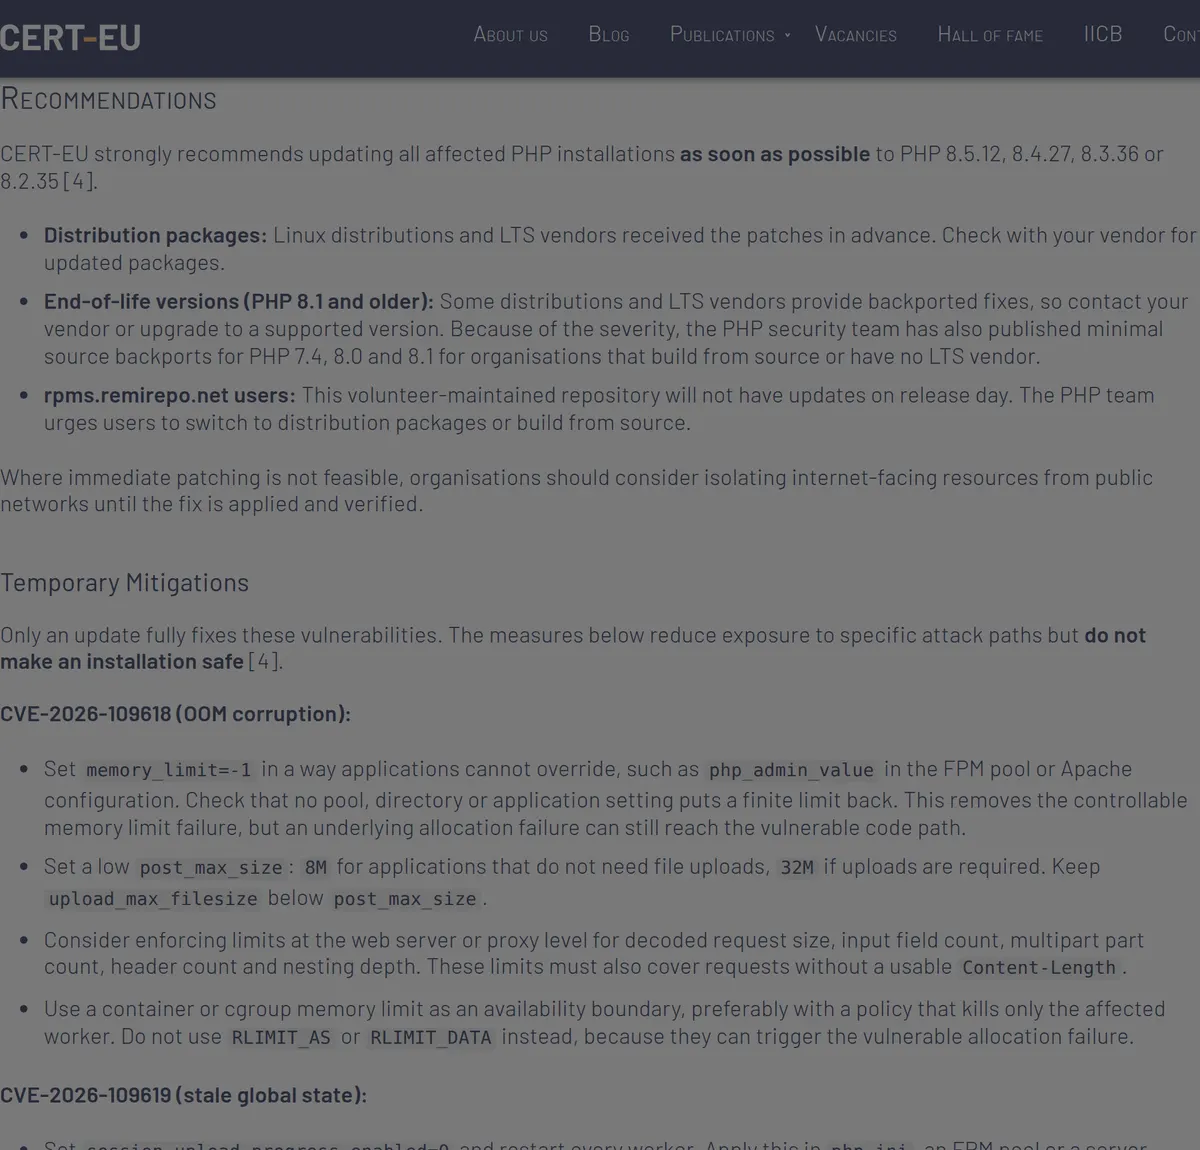
PHP 8.1 and older get no official update. The PHP team posted minimal source backports for 7.4, 8.0 and 8.1, and some Linux distributions and long-term-support vendors have their own fixes.
Try it: if you have a website on shared hosting, WordPress or a hosting control panel, check which PHP version it runs today. It should be 8.5.12, 8.4.27, 8.3.36 or 8.2.35 or newer. If it's older, update it or ask your host. OpenAI posted a free checker that can test a site's address or the PHP installed on a server, and you can run it as a Codex skill or on its own. If you can't update yet, the agencies' advice is to take the site offline until you can.
Affiliate disclosure: some stories use affiliate or referral links. When a link pays a commission, the sentence next to it says so. Sponsored slots are labeled Sponsored. The channel card is a house ad until a sponsor is booked.
Newsletter
Join the waitlist and we'll email you when the first issue launches.
By submitting you agree to our Privacy Policy.
You're on the list after you confirm. We'll email you when the newsletter launches. You can leave from any message. The form posts to Resend.